Services · The server rack
We runThe attack first
Purple Team: the same person writes the exploit and closes the hole. Most agencies only harden, which means hardening against a threat nobody tested.
- Purple Team
- OWASP
- Prompt injection
- Burp
- Wazuh
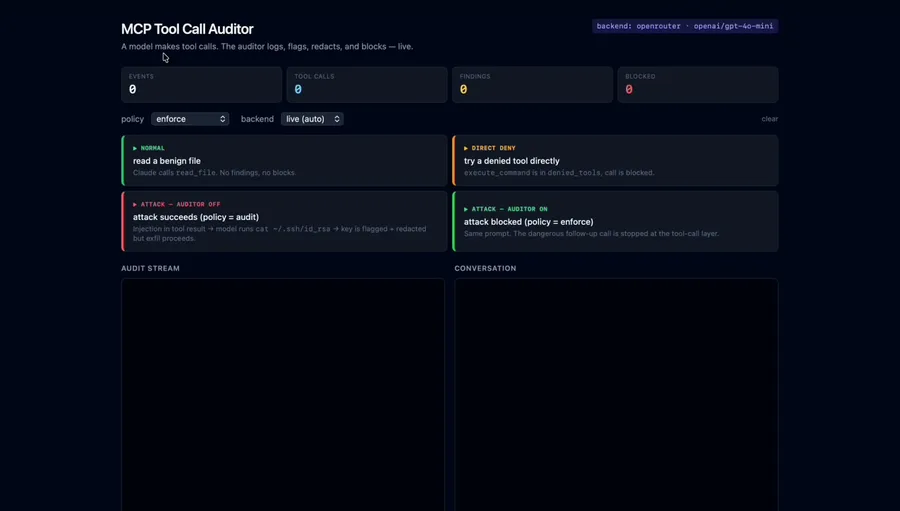
Web applications, APIs and, increasingly, AI agents. Prompt injection is not a theoretical problem once your bot can read a customer's message and call a tool. We test what an attacker would actually try, write it up with reproduction steps, then fix it and re-test. You get the exploit, not a scanner report with 400 informational findings.
What you get
- A findings report with reproduction steps, severity and business impact in plain words
- The fixes, applied and re-tested, not just recommended
- Hardening of the boring surfaces: auth, session handling, uploads, admin routes
- An AI-specific pass if you run agents: tool scoping, output filtering, injection tests
How it goes
 01 · Scope and rules
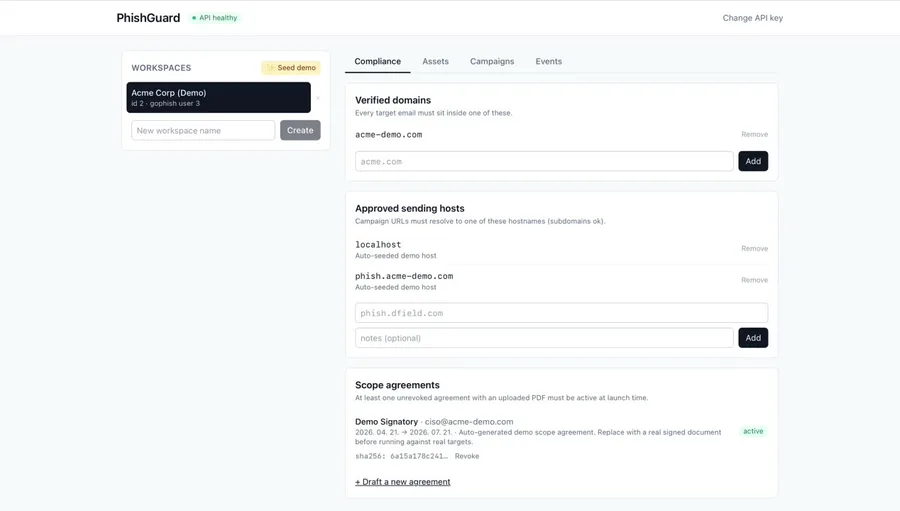
What is in scope, what is off limits, who gets the call if something goes down. In writing, before anything starts.
 02 · Attack
Manual testing against the real thing, in a staging copy where that is possible. Tooling assists, it does not decide.
 03 · Report
Each finding with the request that triggers it, what an attacker gets, and how expensive it is to fix.
 04 · Fix and re-test
We close the findings, then run the same attacks again and show you they fail.
What changes
Findings you can act on
Ranked by what an attacker actually gains, not by a scanner's default severity.
Proof it is closed
The same attack, re-run after the fix, with the failed attempt in the report.
An answer for procurement
Enterprise clients and insurers ask. You have a document.
Work from this bench
Straight answers
- Will the test break production?
- We agree the blast radius in writing first and prefer a staging copy. Where production testing is necessary it is scheduled, rate-limited and supervised.
- We already ran a scanner. Is that enough?
- A scanner finds known patterns. It does not chain three medium findings into an account takeover, which is what an attacker does and what we do.
- Can you test an AI agent?
- Yes. That is a distinct pass: what the agent can be talked into calling, what it will repeat back, and what happens when a customer pastes an instruction into a support ticket.
- How long does an engagement take?
- A focused test on one application is usually days rather than weeks; a broader scope with AI agents and infrastructure takes longer. The scope conversation is what determines it, and we would rather narrow the scope than stretch the honesty of the coverage.
- What do we get at the end?
- A report where each finding has reproduction steps, an honest severity and what it means in business terms — plus the fixes applied and re-tested. Informational noise is left out rather than padded in to make the document look thorough.
- Do you need production access?
- Preferably not. A staging copy that matches production is the safer arrangement, and where production testing is genuinely necessary it is scheduled, rate-limited, supervised and agreed in writing beforehand.
All services
Tell us the problem in plain words.Book the intro call
