Case study · 2026 · Security · AI · Custom software
Generic phishing tests get spotted in the first week.Built an AI phishing-simulation tool. Personalised tests fool the team for real, and the NIS2 paperwork writes itself in the background.
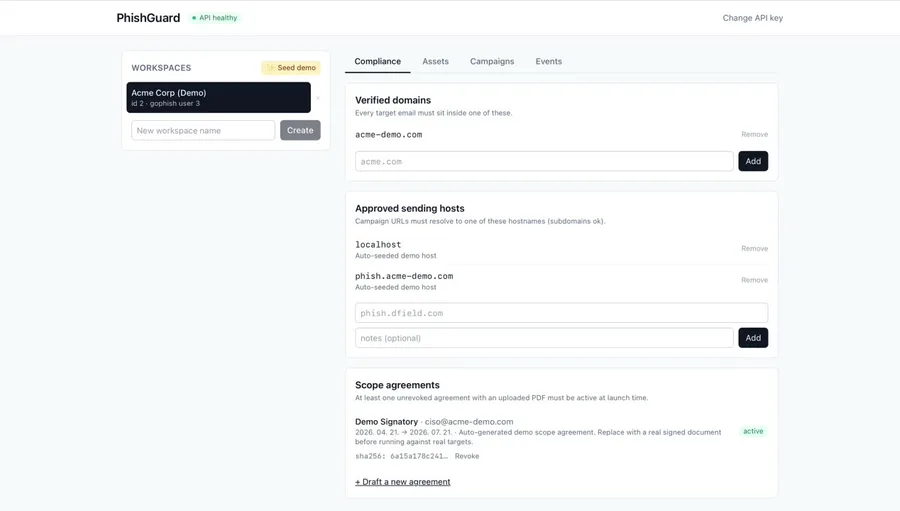
PhisGuard pairs Claude (for context-aware campaign authoring) with Gophish (for delivery) and a Fastify backend (for tracking + automated micro-training). The studio shipped the AI authoring layer, the click + credential capture pipeline, and the NIS2-shaped CISO report.
- TypeScript
- Fastify
- PostgreSQL
- Anthropic
- Go
- Gophish
Inside the build
Overview
- 1/employee
- Tailored scenario
- <5 min
- Training after click
- NIS2
- Report shape
- Q→Q
- Trend tracked per quarter
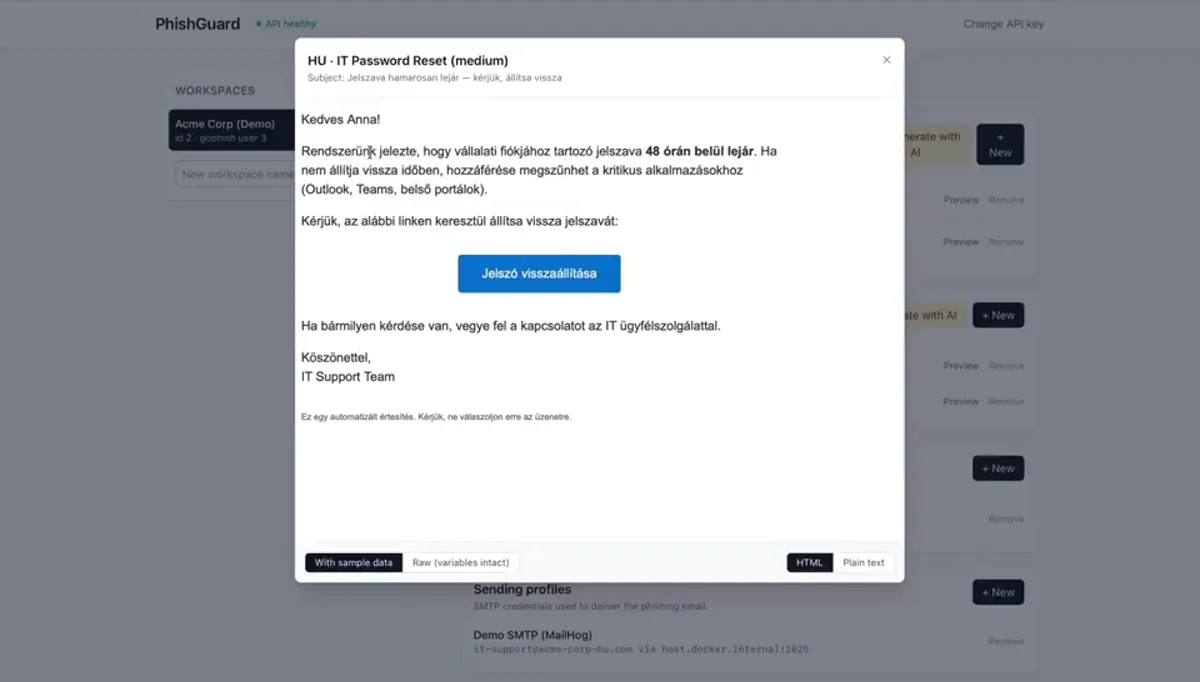
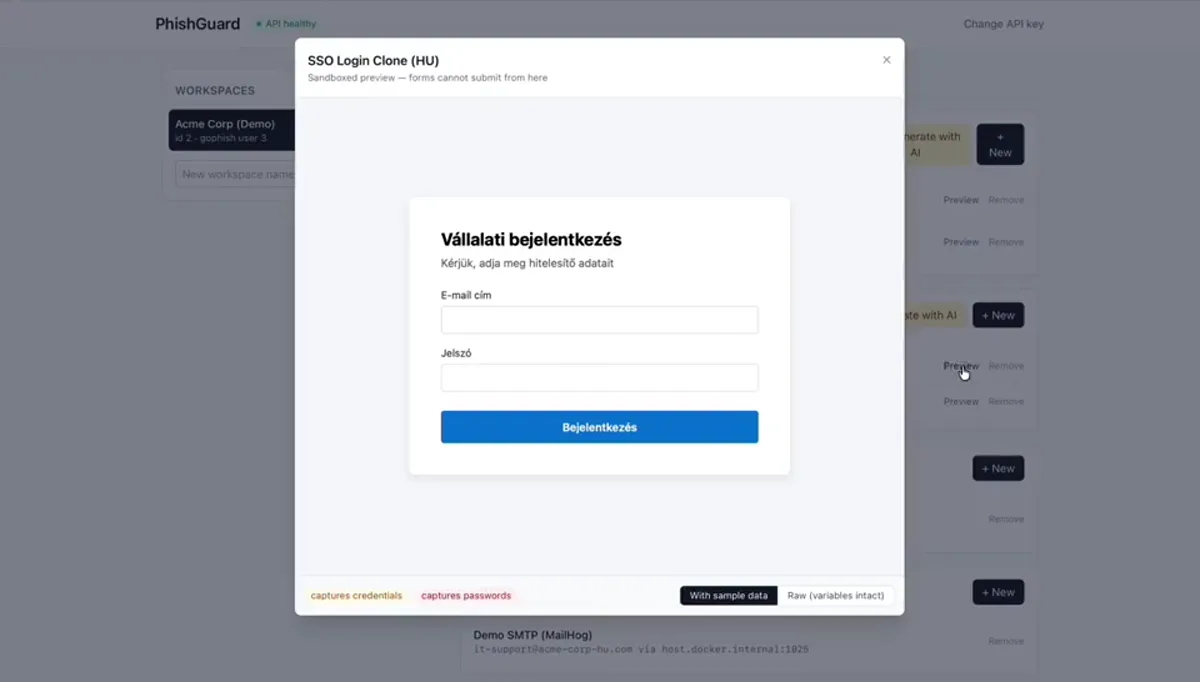
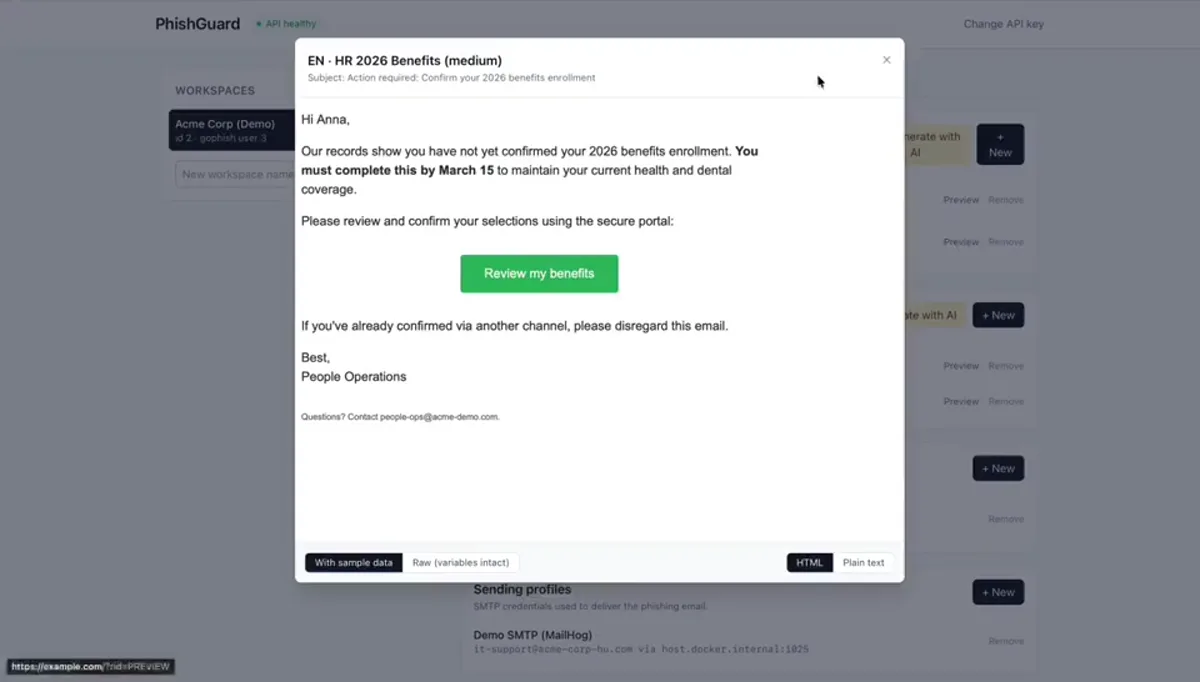
PhisGuard generates realistic phishing campaigns automatically · Claude drafts emails based on the company name, context, and current news, the Gophish (Go) engine delivers them, the Fastify backend tracks clicks and credential entry, and pushes the victim into a 5-minute targeted micro-training on click. NIS2 compliance and employee awareness in one loop.
What shipped
What it does
- AI-generated campaigns · a different scenario per employee, grounded in company context
- Gophish-based engine · stable Go engine for delivery, landing pages, credential capture
- Real-time tracking · who clicked, who entered credentials, who caught it
- Automated micro-learning · whoever clicks gets a 5-minute training within the hour
- NIS2-ready report · for CISO, HR, regulators (MNB / supervisory)
The problem
- Classic KnowBe4 campaigns are the same for everyone · easy to spot
- NIS2 requires recurring awareness training · not maintainable manually
- Training is only valuable right after a fail · emailed PDFs go unread
- No objective metric showing the team actually learns
Why it matters
- Tailored campaigns · real metric for the company's current maturity
- Human-in-the-loop learning · 5-min training at the moment of failure
- NIS2-compliance documentation · CISO audit-ready
- Trajectory · quarter-over-quarter measurable drop in click-through
How it shipped
- 01 · BRIEF
Beat the KnowBe4 'everyone gets the same' problem.
Per-employee scenarios scoped: company name, current news, role-aware vocabulary. Every campaign is unique to the recipient · no two employees see the same lure.
- 02 · BUILD
Claude → Gophish → Fastify capture loop.
Claude drafts personalised emails grounded on company context, Gophish delivers + serves the landing pages, Fastify catches clicks and credentials, and pushes the offender into a 5-minute targeted training within the hour.
- 03 · SHIP
Live on a customer org · NIS2 export ready.
First org rolled out · campaign cadence quarterly, automated micro-learning on every click, CISO export shaped to NIS2 + ISO 27001 evidence requirements.
Stack
AI authoring
Per-employee phishing scenarios
Claude drafts the lure based on company context + role + current news · 'department-wide same email' is gone.
Capture
Gophish + Fastify tracking pipeline
Click, hover, credential entry, and report-as-phish all logged · per-recipient, timestamped, exportable.
Micro-training
5-min targeted lesson on click
The training fires while the failure is still fresh · response rate beats emailed PDFs by an order of magnitude.
NIS2
CISO export shaped to the directive
One-click report mapping the campaign data to NIS2 evidence + ISO 27001 controls · audit-ready, no spreadsheet bridging.
Case study
“We needed phishing tests that actually fool people, plus the NIS2 paperwork that auditors love. PhisGuard does both, the AI-tailored emails actually trick the team, they learn from getting caught, and the security report we hand to the auditor writes itself in the background. We didn't have to rewrite a single line.”